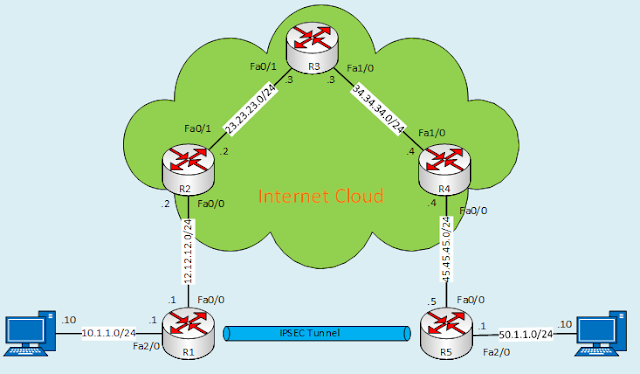
PC1:-
PC1> show ip
NAME :
PC1[1]
PC1[1]
IP/MASK :
10.1.1.10/24
10.1.1.10/24
GATEWAY :
10.1.1.1
10.1.1.1
DNS :
MAC :
00:50:79:66:68:00
00:50:79:66:68:00
LPORT : 10005
RHOST:PORT :
127.0.0.1:10004
127.0.0.1:10004
MTU: : 1500
R1:-
interface FastEthernet0/0
description ***
Connected to R2 ***
Connected to R2 ***
ip address
12.12.12.1 255.255.255.0
12.12.12.1 255.255.255.0
no shut
interface FastEthernet2/0
description *** Connected to PC1 ***
ip address
10.1.1.1 255.255.255.0
10.1.1.1 255.255.255.0
no shut
ip
route 0.0.0.0 0.0.0.0 12.12.12.2
\Default route towards
Internet \
route 0.0.0.0 0.0.0.0 12.12.12.2
\Default route towards
Internet \
crypto isakmp policy 1
\Phase 1 parameters \
\Phase 1 parameters \
encr 3des
hash md5
authentication
pre-share
pre-share
group 2
crypto isakmp key EncryKey address 45.45.45.5 \EncryKey is the pre share key.must
match on both side
match on both side
crypto ipsec transform-set VPN_R1_R5 esp-3des esp-md5-hmac \ Phase 2 Parameters \
crypto map ipsec__R1_R5 10 ipsec-isakmp
set peer
45.45.45.5
\Peer router IP
address \
45.45.45.5
\Peer router IP
address \
set transform-set VPN_R1_R5
match address Client_traffic
ip access-list extended Client_traffic
permit ip 10.1.1.0
0.0.0.255 50.1.1.0 0.0.0.255 \interesting traffic allowed on
IPsec tunnel \
0.0.0.255 50.1.1.0 0.0.0.255 \interesting traffic allowed on
IPsec tunnel \
interface FastEthernet0/0
crypto map ipsec__R1_R5
\Called crypto map
under internet facing interface \
\Called crypto map
under internet facing interface \
no shut
R2:-
interface FastEthernet0/0
description *** Connected to R1 ***
ip address
12.12.12.2 255.255.255.0
12.12.12.2 255.255.255.0
no shut
interface FastEthernet0/1
description *** Connected to R3 ***
ip address
23.23.23.2 255.255.255.0
23.23.23.2 255.255.255.0
no shut
router eigrp 1 \ Used to provide connectivity
between R2 to R4 only \
between R2 to R4 only \
network 12.12.12.2
0.0.0.0
0.0.0.0
network 23.23.23.2
0.0.0.0
0.0.0.0
R3:-
interface FastEthernet0/1
description *** Connected to R2 ***
ip address
23.23.23.3 255.255.255.0
23.23.23.3 255.255.255.0
no shut
interface FastEthernet1/0
description *** Connected to R4 ***
ip address
34.34.34.3 255.255.255.0
34.34.34.3 255.255.255.0
no shut
router eigrp 1
network 23.23.23.3
0.0.0.0
0.0.0.0
network 34.34.34.3
0.0.0.0
0.0.0.0
R4:-
interface FastEthernet0/0
description *** Connected to R5 ***
ip address
45.45.45.4 255.255.255.0
45.45.45.4 255.255.255.0
speed auto
duplex auto
interface FastEthernet1/0
description *** Connected to R3 ***
ip address
34.34.34.4 255.255.255.0
34.34.34.4 255.255.255.0
no shut
router eigrp 1
network 34.34.34.4
0.0.0.0
0.0.0.0
network 45.45.45.4
0.0.0.0
0.0.0.0
R5:-
interface FastEthernet0/0
description ***
Connected to R4 ***
Connected to R4 ***
ip address
45.45.45.5 255.255.255.0
45.45.45.5 255.255.255.0
interface FastEthernet2/0
description *** Connected to PC2 ***
ip address
50.1.1.1 255.255.255.0
50.1.1.1 255.255.255.0
no shut
ip route 0.0.0.0 0.0.0.0 45.45.45.4 \Default route towards Internet \
crypto isakmp policy 1 \Phase 1 parameters \
encr 3des
hash md5
authentication
pre-share
pre-share
group 2
crypto isakmp key EncryKey address 12.12.12.1 \EncryKey is the pre share key.must match on both side
crypto ipsec transform-set VPN_R1_R5 esp-3des
esp-md5-hmac \ Phase 2
Parameters \
esp-md5-hmac \ Phase 2
Parameters \
crypto map ipsec__R1_R5 10 ipsec-isakmp
set peer
12.12.12.1 \Peer router IP address \
12.12.12.1 \Peer router IP address \
set transform-set
VPN_R1_R5
VPN_R1_R5
match address
Client_traffic
Client_traffic
interface FastEthernet0/0
crypto map ipsec__R1_R5
ip access-list extended Client_traffic
permit ip 50.1.1.0 0.0.0.255 10.1.1.0 0.0.0.255 \interesting traffic allowed on IPsec tunnel \
PC2:-
PC2> show ip
NAME :
PC2[1]
PC2[1]
IP/MASK :
50.1.1.10/24
50.1.1.10/24
GATEWAY :
50.1.1.1
50.1.1.1
DNS :
MAC :
00:50:79:66:68:01
00:50:79:66:68:01
LPORT : 10011
RHOST:PORT :
127.0.0.1:10010
127.0.0.1:10010
MTU: : 1500
Verification:-
PC1:-
PC1> ping 50.1.1.10 \ Able to ping PC2 \
84 bytes from 50.1.1.10 icmp_seq=1 ttl=62 time=109.170 ms
84 bytes from 50.1.1.10 icmp_seq=2 ttl=62 time=140.362 ms
84 bytes from 50.1.1.10 icmp_seq=3 ttl=62 time=93.574 ms
84 bytes from 50.1.1.10 icmp_seq=4 ttl=62 time=109.169 ms
84 bytes from 50.1.1.10 icmp_seq=5 ttl=62 time=124.765 ms
PC1> trace 50.1.1.10
trace to 50.1.1.10, 8 hops max, press Ctrl+C to stop
1 10.1.1.1
46.787 ms 15.596 ms 15.596 ms
46.787 ms 15.596 ms 15.596 ms
2 *
* *
* *
3 *50.1.1.10
171.553 ms (ICMP type:3, code:3, Destination port unreachable)
171.553 ms (ICMP type:3, code:3, Destination port unreachable)
R1:-
R1#show crypto isakmp sa \ Phase 1 verfication \
dst
src state conn-id slot status
src state conn-id slot status
45.45.45.5
12.12.12.1 QM_IDLE 1 0 ACTIVE
\ QM_Idle is good \
12.12.12.1 QM_IDLE 1 0 ACTIVE
\ QM_Idle is good \
R1#show crypto ipsec sa
interface: FastEthernet0/0
Crypto map tag: ipsec__R1_R5, local addr
12.12.12.1
12.12.12.1
protected vrf:
(none)
(none)
local ident (addr/mask/prot/port):
(10.1.1.0/255.255.255.0/0/0) \interesting source traffic \
(10.1.1.0/255.255.255.0/0/0) \interesting source traffic \
remote ident (addr/mask/prot/port):
(50.1.1.0/255.255.255.0/0/0) \interesting destination traffic \
(50.1.1.0/255.255.255.0/0/0) \interesting destination traffic \
current_peer
45.45.45.5 port 500
45.45.45.5 port 500
PERMIT,
flags={origin_is_acl,}
flags={origin_is_acl,}
#pkts encaps: 4, #pkts encrypt:
4, #pkts digest: 4 \ Shows encrypted and decrypted packets \
4, #pkts digest: 4 \ Shows encrypted and decrypted packets \
#pkts decaps: 4, #pkts decrypt: 4, #pkts
verify: 4
verify: 4
#pkts
compressed: 0, #pkts decompressed: 0
compressed: 0, #pkts decompressed: 0
#pkts not
compressed: 0, #pkts compr. failed: 0
compressed: 0, #pkts compr. failed: 0
#pkts not
decompressed: 0, #pkts decompress failed: 0
decompressed: 0, #pkts decompress failed: 0
#send errors 0,
#recv errors 0
#recv errors 0
local crypto endpt.: 12.12.12.1,
remote crypto endpt.: 45.45.45.5 \ Tunnel end points \
remote crypto endpt.: 45.45.45.5 \ Tunnel end points \
path mtu 1500,
ip mtu 1500, ip mtu idb FastEthernet0/0
ip mtu 1500, ip mtu idb FastEthernet0/0
current
outbound spi: 0xFB8DE8A1(4220381345)
outbound spi: 0xFB8DE8A1(4220381345)
inbound esp
sas:
sas:
spi:
0xF4E3ADA1(4108561825)
0xF4E3ADA1(4108561825)
transform:
esp-3des esp-md5-hmac ,
esp-3des esp-md5-hmac ,
in use
settings ={Tunnel, }
settings ={Tunnel, }
conn id:
2003, flow_id: SW:3, crypto map: ipsec__R1_R5
2003, flow_id: SW:3, crypto map: ipsec__R1_R5
sa timing:
remaining key lifetime (k/sec): (4501412/3567)
remaining key lifetime (k/sec): (4501412/3567)
IV size: 8
bytes
bytes
replay
detection support: Y
detection support: Y
Status: ACTIVE \ Phase2 is up \
inbound ah
sas:
sas:
inbound pcp
sas:
sas:
outbound esp
sas:
sas:
spi:
0xFB8DE8A1(4220381345)
0xFB8DE8A1(4220381345)
transform:
esp-3des esp-md5-hmac ,
esp-3des esp-md5-hmac ,
in use
settings ={Tunnel, }
settings ={Tunnel, }
conn id:
2002, flow_id: SW:2, crypto map: ipsec__R1_R5
2002, flow_id: SW:2, crypto map: ipsec__R1_R5
sa timing:
remaining key lifetime (k/sec): (4501412/3565)
remaining key lifetime (k/sec): (4501412/3565)
IV size: 8
bytes
bytes
replay
detection support: Y
detection support: Y
Status: ACTIVE \ Phase2 is up \
outbound ah
sas:
sas:
outbound pcp
sas:
sas:
R1#sh ip access-lists
Extended IP access list Client_traffic
10 permit ip
10.1.1.0 0.0.0.255 50.1.1.0 0.0.0.255 (8 matches) \ ACL hit count shows that traffic is hitting Router \
10.1.1.0 0.0.0.255 50.1.1.0 0.0.0.255 (8 matches) \ ACL hit count shows that traffic is hitting Router \
R1#sh ip route
Codes: C – connected, S – static, R – RIP, M – mobile, B
– BGP
– BGP
D – EIGRP,
EX – EIGRP external, O – OSPF, IA – OSPF inter area
EX – EIGRP external, O – OSPF, IA – OSPF inter area
N1 – OSPF
NSSA external type 1, N2 – OSPF NSSA external type 2
NSSA external type 1, N2 – OSPF NSSA external type 2
E1 – OSPF
external type 1, E2 – OSPF external type 2
external type 1, E2 – OSPF external type 2
i – IS-IS,
su – IS-IS summary, L1 – IS-IS level-1, L2 – IS-IS level-2
su – IS-IS summary, L1 – IS-IS level-1, L2 – IS-IS level-2
ia – IS-IS
inter area, * – candidate default, U – per-user static route
inter area, * – candidate default, U – per-user static route
o – ODR, P –
periodic downloaded static route
periodic downloaded static route
Gateway of last resort is 12.12.12.2 to network 0.0.0.0
10.0.0.0/24 is
subnetted, 1 subnets
subnetted, 1 subnets
C 10.1.1.0 is
directly connected, FastEthernet2/0
directly connected, FastEthernet2/0
12.0.0.0/24 is
subnetted, 1 subnets
subnetted, 1 subnets
C 12.12.12.0
is directly connected, FastEthernet0/0
is directly connected, FastEthernet0/0
S* 0.0.0.0/0
[1/0] via 12.12.12.2
[1/0] via 12.12.12.2
R2:-
R2#sh ip eigrp neighbors
EIGRP-IPv4 Neighbors for AS(1)
H Address Interface Hold Uptime SRTT
RTO Q Seq
RTO Q Seq
(sec) (ms) Cnt Num
0 23.23.23.3 Fa0/1 14 01:22:19 41
246 0 8
246 0 8
R2#sh ip route
Codes: L – local, C – connected, S – static, R – RIP, M –
mobile, B – BGP
mobile, B – BGP
D – EIGRP,
EX – EIGRP external, O – OSPF, IA – OSPF inter area
EX – EIGRP external, O – OSPF, IA – OSPF inter area
N1 – OSPF
NSSA external type 1, N2 – OSPF NSSA external type 2
NSSA external type 1, N2 – OSPF NSSA external type 2
E1 – OSPF
external type 1, E2 – OSPF external type 2
external type 1, E2 – OSPF external type 2
i – IS-IS,
su – IS-IS summary, L1 – IS-IS level-1, L2 – IS-IS level-2
su – IS-IS summary, L1 – IS-IS level-1, L2 – IS-IS level-2
ia – IS-IS
inter area, * – candidate default, U – per-user static route
inter area, * – candidate default, U – per-user static route
o – ODR, P –
periodic downloaded static route, H – NHRP
periodic downloaded static route, H – NHRP
+ –
replicated route, % – next hop override
replicated route, % – next hop override
Gateway of last resort is not set
12.0.0.0/8 is
variably subnetted, 2 subnets, 2 masks
variably subnetted, 2 subnets, 2 masks
C
12.12.12.0/24 is directly connected, FastEthernet0/0
12.12.12.0/24 is directly connected, FastEthernet0/0
L
12.12.12.2/32 is directly connected, FastEthernet0/0
12.12.12.2/32 is directly connected, FastEthernet0/0
23.0.0.0/8 is
variably subnetted, 2 subnets, 2 masks
variably subnetted, 2 subnets, 2 masks
C
23.23.23.0/24 is directly connected, FastEthernet0/1
23.23.23.0/24 is directly connected, FastEthernet0/1
L
23.23.23.2/32 is directly connected, FastEthernet0/1
23.23.23.2/32 is directly connected, FastEthernet0/1
34.0.0.0/24
is subnetted, 1 subnets
is subnetted, 1 subnets
D 34.34.34.0
[90/30720] via 23.23.23.3, 01:22:14, FastEthernet0/1
[90/30720] via 23.23.23.3, 01:22:14, FastEthernet0/1
45.0.0.0/24
is subnetted, 1 subnets
is subnetted, 1 subnets
D 45.45.45.0
[90/33280] via 23.23.23.3, 01:21:20, FastEthernet0/1
[90/33280] via 23.23.23.3, 01:21:20, FastEthernet0/1
R2#sh cdp neighbors
Capability Codes: R – Router, T – Trans Bridge, B –
Source Route Bridge
Source Route Bridge
S
– Switch, H – Host, I – IGMP, r – Repeater, P – Phone
– Switch, H – Host, I – IGMP, r – Repeater, P – Phone
Device ID
Local Intrfce Holdtme Capability
Platform Port ID
Local Intrfce Holdtme Capability
Platform Port ID
R3
Fas 0/1 174 R 7206VXR
Fas 0/1
Fas 0/1 174 R 7206VXR
Fas 0/1
R1 Fas
0/0 163
R S I 3745 Fas 0/0
0/0 163
R S I 3745 Fas 0/0
R3:-
R3#sh ip eigrp neighbors
EIGRP-IPv4 Neighbors for AS(1)
H Address Interface Hold Uptime SRTT
RTO Q Seq
RTO Q Seq
(sec) (ms) Cnt Num
1 34.34.34.4 Fa1/0 11 01:21:53 47
282 0 4
282 0 4
0 23.23.23.2 Fa0/1 12 01:22:47 1035 5000
0 4
0 4
R3#sh ip route
Codes: L – local, C – connected, S – static, R – RIP, M –
mobile, B – BGP
mobile, B – BGP
D – EIGRP,
EX – EIGRP external, O – OSPF, IA – OSPF inter area
EX – EIGRP external, O – OSPF, IA – OSPF inter area
N1 – OSPF
NSSA external type 1, N2 – OSPF NSSA external type 2
NSSA external type 1, N2 – OSPF NSSA external type 2
E1 – OSPF
external type 1, E2 – OSPF external type 2
external type 1, E2 – OSPF external type 2
i – IS-IS,
su – IS-IS summary, L1 – IS-IS level-1, L2 – IS-IS level-2
su – IS-IS summary, L1 – IS-IS level-1, L2 – IS-IS level-2
ia – IS-IS
inter area, * – candidate default, U – per-user static route
inter area, * – candidate default, U – per-user static route
o – ODR, P –
periodic downloaded static route, H – NHRP
periodic downloaded static route, H – NHRP
+ –
replicated route, % – next hop override
replicated route, % – next hop override
Gateway of last resort is not set
12.0.0.0/24
is subnetted, 1 subnets
is subnetted, 1 subnets
D 12.12.12.0
[90/30720] via 23.23.23.2, 01:22:48, FastEthernet0/1
[90/30720] via 23.23.23.2, 01:22:48, FastEthernet0/1
23.0.0.0/8 is
variably subnetted, 2 subnets, 2 masks
variably subnetted, 2 subnets, 2 masks
C
23.23.23.0/24 is directly connected, FastEthernet0/1
23.23.23.0/24 is directly connected, FastEthernet0/1
L
23.23.23.3/32 is directly connected, FastEthernet0/1
23.23.23.3/32 is directly connected, FastEthernet0/1
34.0.0.0/8 is
variably subnetted, 2 subnets, 2 masks
variably subnetted, 2 subnets, 2 masks
C
34.34.34.0/24 is directly connected, FastEthernet1/0
34.34.34.0/24 is directly connected, FastEthernet1/0
L
34.34.34.3/32 is directly connected, FastEthernet1/0
34.34.34.3/32 is directly connected, FastEthernet1/0
45.0.0.0/24
is subnetted, 1 subnets
is subnetted, 1 subnets
D 45.45.45.0
[90/30720] via 34.34.34.4, 01:21:49, FastEthernet1/0
[90/30720] via 34.34.34.4, 01:21:49, FastEthernet1/0
R4:-
R4#sh ip eigrp neighbors
EIGRP-IPv4 Neighbors for AS(1)
H Address Interface Hold Uptime SRTT
RTO Q Seq
RTO Q Seq
(sec) (ms) Cnt Num
0 34.34.34.3 Fa1/0 14 01:59:20 1270 5000
0 7
0 7
R4#sh ip route
Codes: L – local, C – connected, S – static, R – RIP, M –
mobile, B – BGP
mobile, B – BGP
D – EIGRP,
EX – EIGRP external, O – OSPF, IA – OSPF inter area
EX – EIGRP external, O – OSPF, IA – OSPF inter area
N1 – OSPF
NSSA external type 1, N2 – OSPF NSSA external type 2
NSSA external type 1, N2 – OSPF NSSA external type 2
E1 – OSPF
external type 1, E2 – OSPF external type 2
external type 1, E2 – OSPF external type 2
i – IS-IS,
su – IS-IS summary, L1 – IS-IS level-1, L2 – IS-IS level-2
su – IS-IS summary, L1 – IS-IS level-1, L2 – IS-IS level-2
ia – IS-IS
inter area, * – candidate default, U – per-user static route
inter area, * – candidate default, U – per-user static route
o – ODR, P –
periodic downloaded static route, H – NHRP
periodic downloaded static route, H – NHRP
+ –
replicated route, % – next hop override
replicated route, % – next hop override
Gateway of last resort is not set
12.0.0.0/24
is subnetted, 1 subnets
is subnetted, 1 subnets
D 12.12.12.0
[90/33280] via 34.34.34.3, 01:59:21, FastEthernet1/0
[90/33280] via 34.34.34.3, 01:59:21, FastEthernet1/0
23.0.0.0/24
is subnetted, 1 subnets
is subnetted, 1 subnets
D 23.23.23.0
[90/30720] via 34.34.34.3, 01:59:21, FastEthernet1/0
[90/30720] via 34.34.34.3, 01:59:21, FastEthernet1/0
34.0.0.0/8 is
variably subnetted, 2 subnets, 2 masks
variably subnetted, 2 subnets, 2 masks
C 34.34.34.0/24
is directly connected, FastEthernet1/0
is directly connected, FastEthernet1/0
L
34.34.34.4/32 is directly connected, FastEthernet1/0
34.34.34.4/32 is directly connected, FastEthernet1/0
45.0.0.0/8 is
variably subnetted, 2 subnets, 2 masks
variably subnetted, 2 subnets, 2 masks
C
45.45.45.0/24 is directly connected, FastEthernet0/0
45.45.45.0/24 is directly connected, FastEthernet0/0
L
45.45.45.4/32 is directly connected, FastEthernet0/0
45.45.45.4/32 is directly connected, FastEthernet0/0
R5:-
R5#sh ip route
Codes: C – connected, S – static, R – RIP, M – mobile, B
– BGP
– BGP
D – EIGRP,
EX – EIGRP external, O – OSPF, IA – OSPF inter area
EX – EIGRP external, O – OSPF, IA – OSPF inter area
N1 – OSPF
NSSA external type 1, N2 – OSPF NSSA external type 2
NSSA external type 1, N2 – OSPF NSSA external type 2
E1 – OSPF
external type 1, E2 – OSPF external type 2
external type 1, E2 – OSPF external type 2
i – IS-IS,
su – IS-IS summary, L1 – IS-IS level-1, L2 – IS-IS level-2
su – IS-IS summary, L1 – IS-IS level-1, L2 – IS-IS level-2
ia – IS-IS
inter area, * – candidate default, U – per-user static route
inter area, * – candidate default, U – per-user static route
o – ODR, P –
periodic downloaded static route
periodic downloaded static route
Gateway of last resort is 45.45.45.4 to network 0.0.0.0
50.0.0.0/24 is
subnetted, 1 subnets
subnetted, 1 subnets
C 50.1.1.0 is
directly connected, FastEthernet2/0
directly connected, FastEthernet2/0
45.0.0.0/24 is
subnetted, 1 subnets
subnetted, 1 subnets
C 45.45.45.0
is directly connected, FastEthernet0/0
is directly connected, FastEthernet0/0
S* 0.0.0.0/0
[1/0] via 45.45.45.4
[1/0] via 45.45.45.4
R5#sh crypto isakmp sa
\ Phase1 is up \
\ Phase1 is up \
dst
src state conn-id slot status
src state conn-id slot status
45.45.45.5
12.12.12.1 QM_IDLE 1 0 ACTIVE
12.12.12.1 QM_IDLE 1 0 ACTIVE
R5#show crypto ipsec sa
interface: FastEthernet0/0
Crypto map tag:
ipsec__R1_R5, local addr 45.45.45.5
ipsec__R1_R5, local addr 45.45.45.5
protected vrf:
(none)
(none)
local ident (addr/mask/prot/port):
(50.1.1.0/255.255.255.0/0/0)
(50.1.1.0/255.255.255.0/0/0)
remote ident
(addr/mask/prot/port): (10.1.1.0/255.255.255.0/0/0)
(addr/mask/prot/port): (10.1.1.0/255.255.255.0/0/0)
current_peer
12.12.12.1 port 500
12.12.12.1 port 500
PERMIT,
flags={origin_is_acl,}
flags={origin_is_acl,}
#pkts encaps: 22, #pkts encrypt:
22, #pkts digest: 22 \ Number of packets encrypted \
22, #pkts digest: 22 \ Number of packets encrypted \
#pkts decaps: 22, #pkts decrypt: 22, #pkts
verify: 22 \ Number of packets decrypted \
verify: 22 \ Number of packets decrypted \
#pkts
compressed: 0, #pkts decompressed: 0
compressed: 0, #pkts decompressed: 0
#pkts not
compressed: 0, #pkts compr. failed: 0
compressed: 0, #pkts compr. failed: 0
#pkts not
decompressed: 0, #pkts decompress failed: 0
decompressed: 0, #pkts decompress failed: 0
#send errors 2,
#recv errors 0
#recv errors 0
local crypto endpt.: 45.45.45.5,
remote crypto endpt.: 12.12.12.1
\ Tunnel end points \
remote crypto endpt.: 12.12.12.1
\ Tunnel end points \
path mtu 1500,
ip mtu 1500, ip mtu idb FastEthernet0/0
ip mtu 1500, ip mtu idb FastEthernet0/0
current
outbound spi: 0xF4E3ADA1(4108561825)
outbound spi: 0xF4E3ADA1(4108561825)
inbound esp
sas:
sas:
spi:
0xFB8DE8A1(4220381345)
0xFB8DE8A1(4220381345)
transform:
esp-3des esp-md5-hmac ,
esp-3des esp-md5-hmac ,
in use
settings ={Tunnel, }
settings ={Tunnel, }
conn id:
2003, flow_id: SW:3, crypto map: ipsec__R1_R5
2003, flow_id: SW:3, crypto map: ipsec__R1_R5
sa timing:
remaining key lifetime (k/sec): (4607263/1083)
remaining key lifetime (k/sec): (4607263/1083)
IV size: 8
bytes
bytes
replay
detection support: Y
detection support: Y
Status:
ACTIVE \ Phase2 is up \
ACTIVE \ Phase2 is up \
inbound ah
sas:
sas:
inbound pcp
sas:
sas:
outbound esp
sas:
sas:
spi:
0xF4E3ADA1(4108561825)
0xF4E3ADA1(4108561825)
transform:
esp-3des esp-md5-hmac ,
esp-3des esp-md5-hmac ,
in use
settings ={Tunnel, }
settings ={Tunnel, }
conn id:
2002, flow_id: SW:2, crypto map: ipsec__R1_R5
2002, flow_id: SW:2, crypto map: ipsec__R1_R5
sa timing:
remaining key lifetime (k/sec): (4607263/1068)
remaining key lifetime (k/sec): (4607263/1068)
IV size: 8
bytes
bytes
replay
detection support: Y
detection support: Y
Status:
ACTIVE \ Phase2 is up \
ACTIVE \ Phase2 is up \
outbound ah
sas:
sas:
outbound pcp
sas:
sas:
protected vrf:
(none)
(none)
local ident (addr/mask/prot/port):
(10.1.1.0/255.255.255.0/0/0)
(10.1.1.0/255.255.255.0/0/0)
remote ident (addr/mask/prot/port):
(50.1.1.0/255.255.255.0/0/0)
(50.1.1.0/255.255.255.0/0/0)
current_peer
12.12.12.1 port 500
12.12.12.1 port 500
PERMIT,
flags={origin_is_acl,}
flags={origin_is_acl,}
#pkts encaps:
0, #pkts encrypt: 0, #pkts digest: 0
0, #pkts encrypt: 0, #pkts digest: 0
#pkts decaps:
0, #pkts decrypt: 0, #pkts verify: 0
0, #pkts decrypt: 0, #pkts verify: 0
#pkts
compressed: 0, #pkts decompressed: 0
compressed: 0, #pkts decompressed: 0
#pkts not
compressed: 0, #pkts compr. failed: 0
compressed: 0, #pkts compr. failed: 0
#pkts not
decompressed: 0, #pkts decompress failed: 0
decompressed: 0, #pkts decompress failed: 0
#send errors 0,
#recv errors 0
#recv errors 0
local crypto endpt.: 45.45.45.5,
remote crypto endpt.: 12.12.12.1
remote crypto endpt.: 12.12.12.1
path mtu 1500,
ip mtu 1500, ip mtu idb FastEthernet0/0
ip mtu 1500, ip mtu idb FastEthernet0/0
current
outbound spi: 0x0(0)
outbound spi: 0x0(0)
inbound esp
sas:
sas:
inbound ah
sas:
sas:
inbound pcp
sas:
sas:
outbound esp
sas:
sas:
outbound ah
sas:
sas:
outbound pcp
sas:
sas:
protected vrf:
(none)
(none)
local ident (addr/mask/prot/port):
(50.1.1.0/255.255.255.0/10/0)
(50.1.1.0/255.255.255.0/10/0)
remote ident
(addr/mask/prot/port): (10.1.1.0/255.255.255.0/10/0)
(addr/mask/prot/port): (10.1.1.0/255.255.255.0/10/0)
current_peer
12.12.12.1 port 500
12.12.12.1 port 500
PERMIT,
flags={origin_is_acl,}
flags={origin_is_acl,}
#pkts encaps:
0, #pkts encrypt: 0, #pkts digest: 0
0, #pkts encrypt: 0, #pkts digest: 0
#pkts decaps:
0, #pkts decrypt: 0, #pkts verify: 0
0, #pkts decrypt: 0, #pkts verify: 0
#pkts
compressed: 0, #pkts decompressed: 0
compressed: 0, #pkts decompressed: 0
#pkts not
compressed: 0, #pkts compr. failed: 0
compressed: 0, #pkts compr. failed: 0
#pkts not
decompressed: 0, #pkts decompress failed: 0
decompressed: 0, #pkts decompress failed: 0
#send errors 0,
#recv errors 0
#recv errors 0
local crypto
endpt.: 45.45.45.5, remote crypto endpt.: 12.12.12.1
endpt.: 45.45.45.5, remote crypto endpt.: 12.12.12.1
path mtu 1500,
ip mtu 1500, ip mtu idb FastEthernet0/0
ip mtu 1500, ip mtu idb FastEthernet0/0
current
outbound spi: 0x0(0)
outbound spi: 0x0(0)
inbound esp
sas:
sas:
inbound ah
sas:
sas:
inbound pcp
sas:
sas:
outbound esp
sas:
sas:
outbound ah
sas:
sas:
outbound pcp
sas:
sas:
R5#
show crypto session detail
show crypto session detail
Crypto session current status
Code: C – IKE Configuration mode, D – Dead Peer Detection
K – Keepalives, N – NAT-traversal, X – IKE Extended
Authentication
Authentication
Interface: FastEthernet0/0
Session status: UP-ACTIVE
Peer: 12.12.12.1 port 500 fvrf: (none) ivrf: (none)
Phase1_id:
12.12.12.1
12.12.12.1
Desc: (none)
IKE SA: local
45.45.45.5/500 remote 12.12.12.1/500 Active
45.45.45.5/500 remote 12.12.12.1/500 Active
Capabilities:D connid:1 lifetime:22:33:45
IPSEC FLOW:
permit ip 50.1.1.0/255.255.255.0 10.1.1.0/255.255.255.0
permit ip 50.1.1.0/255.255.255.0 10.1.1.0/255.255.255.0
Active SAs:
2, origin: crypto map
2, origin: crypto map
Inbound: #pkts dec’ed 22 drop 0 life (KB/Sec) 4607263/1056
Outbound: #pkts enc’ed 22 drop 2 life
(KB/Sec) 4607263/1056
(KB/Sec) 4607263/1056
IPSEC FLOW:
permit ip 10.1.1.0/255.255.255.0 50.1.1.0/255.255.255.0
permit ip 10.1.1.0/255.255.255.0 50.1.1.0/255.255.255.0
Active SAs:
0, origin: crypto map
0, origin: crypto map
Inbound: #pkts dec’ed 0 drop 0
life (KB/Sec) 0/0
Outbound:
#pkts enc’ed 0 drop 0 life (KB/Sec) 0/0
#pkts enc’ed 0 drop 0 life (KB/Sec) 0/0
IPSEC FLOW:
permit 10 50.1.1.0/255.255.255.0 10.1.1.0/255.255.255.0
permit 10 50.1.1.0/255.255.255.0 10.1.1.0/255.255.255.0
Active SAs:
0, origin: crypto map
0, origin: crypto map
Inbound: #pkts dec’ed 0 drop 0
life (KB/Sec) 0/0
Outbound:
#pkts enc’ed 0 drop 0 life (KB/Sec) 0/0
#pkts enc’ed 0 drop 0 life (KB/Sec) 0/0
R5# ping
10.1.1.1 source 50.1.1.1
10.1.1.1 source 50.1.1.1
Type escape sequence to abort.
Sending 5, 100-byte ICMP Echos to 10.1.1.1, timeout is 2
seconds:
seconds:
Packet sent with a source address of 50.1.1.1
!!!!!
Success rate is 100 percent (5/5), round-trip min/avg/max
= 164/336/940 ms
= 164/336/940 ms
ESW2#show crypto isakmp sa de
Codes: C – IKE configuration mode, D – Dead Peer
Detection
Detection
K –
Keepalives, N – NAT-traversal
Keepalives, N – NAT-traversal
X – IKE
Extended Authentication
Extended Authentication
psk –
Preshared key, rsig – RSA signature
Preshared key, rsig – RSA signature
renc – RSA
encryption
encryption
C-id Local Remote I-VRF Status Encr Hash Auth DH Lifetime Cap.
1
45.45.45.5 12.12.12.1 ACTIVE 3des md5 psk
2 22:21:05
45.45.45.5 12.12.12.1 ACTIVE 3des md5 psk
2 22:21:05
Connection-id:Engine-id =
1:1(software)
PC2:-
PC2> ping 10.1.1.10 \ Able to ping PC1 \
84 bytes from 10.1.1.10 icmp_seq=1 ttl=62 time=77.979 ms
84 bytes from 10.1.1.10 icmp_seq=2 ttl=62 time=124.766 ms
84 bytes from 10.1.1.10 icmp_seq=3 ttl=62 time=140.361 ms
84 bytes from 10.1.1.10 icmp_seq=4 ttl=62 time=155.957 ms
84 bytes from 10.1.1.10 icmp_seq=5 ttl=62 time=109.170 ms
PC2> trace 10.1.1.10
trace to 10.1.1.10, 8 hops max, press Ctrl+C to stop
1 50.1.1.1
15.596 ms 15.595 ms 15.596 ms
15.596 ms 15.595 ms 15.596 ms
2 10.1.1.10
140.361 ms (ICMP type:3, code:3, Destination port unreachable)
140.361 ms (ICMP type:3, code:3, Destination port unreachable)